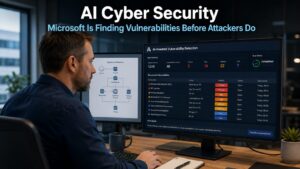
AI cyber security is entering a genuinely new phase, and a recent development from Microsoft illustrates where the technology is heading. Most security tools work reactively. Something suspicious happens, the system identifies it, and then attempts to limit the damage before it spreads further. Microsoft has been developing something that operates differently: using AI to find security weaknesses before attackers can discover and exploit them. The system is called MDASH, and what it has already uncovered during testing is worth understanding.
What MDASH Does and Why It Matters
MDASH is a platform Microsoft built internally that uses more than 100 specialised AI agents working together to search for hidden security flaws inside Windows. Each agent is designed to inspect a different part of the system, test for specific types of weakness, and flag potential vulnerabilities automatically, at a scale and speed that human security engineers could not match through manual review alone.
During testing, MDASH uncovered multiple previously unknown vulnerabilities in important parts of Windows. Some of these flaws were classified as critical. They included weaknesses that attackers could potentially have exploited remotely over the internet, which represents a serious category of risk. Critically identified flaws of this type, if found by attackers before they are patched, can allow remote code execution, the ability to take control of a system from a distance without physical access.
The accuracy of the system is what makes the results particularly notable. One of the persistent problems with AI-driven security tools has been a high rate of false positives: flags that appear to identify genuine issues but turn out to be benign on investigation. This creates significant noise that consumes security team time and gradually reduces confidence in the tool. Microsoft reports that MDASH has been unusually effective at avoiding this problem while still surfacing genuine risks.
The concept of AI agents constantly scanning for hidden vulnerabilities before criminals find them represents a genuinely promising direction for AI cyber security. Attackers invest significant effort in identifying exploitable weaknesses. A system that automates the search for those weaknesses from the defender’s side changes the dynamic of that race in a meaningful way.
Where MDASH Fits in the Current Security Landscape
It is important to keep MDASH in appropriate context. The system is currently being used internally by Microsoft engineers. It is not yet a tool that businesses can deploy directly, and the timeline for broader availability has not been confirmed. Even as AI cyber security capabilities of this kind mature and become more accessible, they will not replace the security fundamentals that protect most businesses today.
Most successful cyber attacks against businesses do not exploit obscure, previously unknown vulnerabilities in operating system code. They succeed through considerably more ordinary gaps: weak or reused passwords, systems that have not been patched, staff who click a link in a phishing email, poor access controls that give too many people access to too much data, and backups that have not been properly maintained or tested.
These are the risks that affect the overwhelming majority of businesses right now. An AI system capable of discovering critical vulnerabilities in Windows code addresses a category of threat that is real and serious, but that sits at a different level of sophistication from the attacks that most businesses across Sussex and the South East face on a daily basis. Our article on why cyber attacks are rising covers the threat landscape as it affects businesses in practice.
Why the Security Fundamentals Remain the Priority
The development of sophisticated AI cyber security tools is encouraging and points to stronger protection in the future. However, none of it changes the calculus for businesses that have not yet addressed the basics.
A business with strong, unique passwords on all accounts, multi-factor authentication enabled across its critical systems, a consistent patching schedule, properly trained staff, and tested backups is already protected against the vast majority of attacks that target businesses of any size. A business that lacks these fundamentals but has access to advanced AI security capabilities has still left the most common doors wide open.
Multi-factor authentication alone addresses one of the most reliable entry routes attackers use: stolen credentials. Our article on strengthening your business security explains how to implement this across your organisation. Password hygiene is covered in our article on secure passwords for business. And the importance of properly maintained backups is covered in our article on immutable backup storage.
These are not exciting or novel recommendations. They are effective ones. The best available evidence consistently shows that businesses which do these things well experience significantly fewer successful attacks than those that do not, regardless of what emerging AI security capabilities exist in parallel.
AI on Both Sides of the Security Equation
MDASH illustrates one side of how AI is changing cyber security. The other side is equally important to acknowledge. AI is also becoming a more capable tool for attackers. Phishing messages are more convincing. Vulnerability scanning at scale is faster. Malware adapts more quickly to evade detection. Our article on AI-powered malware covers how this is already affecting the threat businesses face.
The development of AI cyber security tools like MDASH is a direct response to this reality. As attackers use AI to find weaknesses faster, defenders need equivalent or superior capability to stay ahead. From that perspective, MDASH is not simply an impressive technical achievement. It is part of a necessary arms race in which the stakes for businesses continue to rise.
For most businesses, the practical implication of this arms race is not to seek out the most advanced AI security capabilities available. It is to ensure that the foundations are solid enough that attackers using conventional tools, or even reasonably capable AI-assisted tools, find the usual routes blocked. Our cyber security page covers how a layered, structured approach to security addresses the full range of threats businesses face at different levels of sophistication.
What This Means For Businesses
Microsoft’s MDASH is a significant step in AI cyber security that demonstrates what proactive, AI-driven vulnerability discovery can achieve. It is also a reminder that the security landscape is evolving in ways that will continue to require both technical innovation and basic discipline to navigate effectively.
For business owners and directors, the practical takeaway is the same as it has been for some time, expressed with renewed urgency. Ensure the fundamentals are consistently in place. Patching, strong passwords, multi-factor authentication, access controls, staff awareness, and tested backups are the measures that protect most businesses against most attacks. Advanced AI security capabilities will add further layers of protection as they mature and become accessible. They will not substitute for the basics that too many businesses still have not fully addressed.
Our managed IT services include ongoing security management, patch monitoring, and access control reviews for businesses across Sussex and the South East, ensuring the foundations are properly in place and consistently maintained.
Final Thoughts
The future of AI cyber security is genuinely promising. AI systems that proactively search for vulnerabilities before attackers find them represent a meaningful advance in how defence can work. The present reality is that most businesses are more exposed to ordinary, well-understood attacks than to the novel vulnerabilities that systems like MDASH are designed to uncover.
Good security still comes down to reducing risk, limiting opportunities for attackers, and making sure the simple things are consistently done well. That principle has not changed, and it will not change as AI capabilities on both sides of the equation continue to develop.
MDASH is an internal Microsoft AI system that uses more than 100 specialised AI agents working in parallel to search for hidden security vulnerabilities inside Windows. The agents inspect different parts of the system, test for specific types of weakness, and flag potential flaws automatically. During testing, the system uncovered multiple previously unknown vulnerabilities, including some classified as critical, that could have been exploited remotely if found by attackers first.
Not currently. MDASH is being used internally by Microsoft engineers and is not available for businesses to deploy directly. Its discoveries feed into Microsoft’s security patching process, which means businesses that keep their Windows systems updated benefit indirectly from what the system finds. No timeline for broader access has been confirmed.
No. Most successful attacks against businesses succeed through ordinary gaps: weak passwords, unpatched systems, phishing clicks, poor access controls, and inadequate backups. Advanced AI security tools address a different category of threat. They do not replace the need for strong fundamentals, which remain the most effective protection against the attacks that affect most businesses in practice.
Attackers are using AI to create more convincing phishing emails, scan for vulnerabilities at scale, and build malware that adapts more quickly to evade detection. The development of defensive AI cyber security capabilities like MDASH is in part a response to this evolving attacker capability. For businesses, this reinforces the importance of maintaining strong foundations, as attackers with increasingly capable tools will find those foundations more effective barriers than outdated or inconsistent security practices.
Strong, unique passwords managed through a password manager, multi-factor authentication on all critical accounts, consistent software patching and updates, appropriate access controls limiting what each staff member can reach, regular staff awareness training, and properly maintained and tested backups. These measures address the most common attack routes and are more effective in practice than any single advanced security technology deployed without this foundation in place.