Real Login Page Phishing: Why a Genuine Microsoft Page Is No Longer a Safety Signal
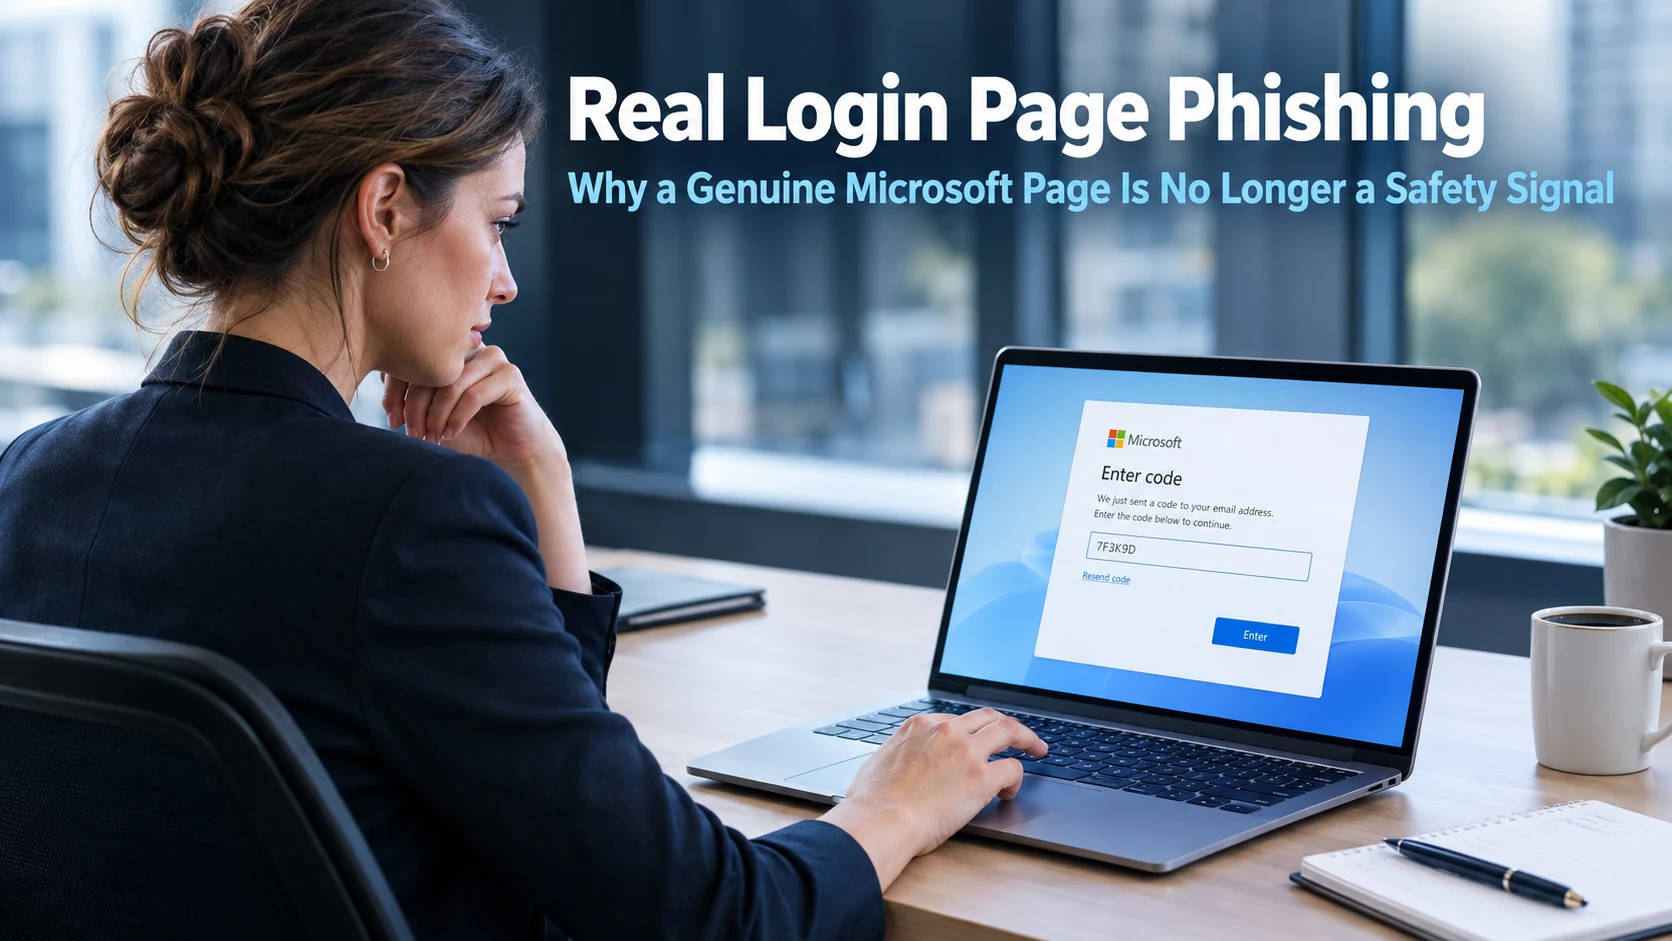
Real login page phishing is one of the most difficult current threats for business teams to spot because it removes the signals that most people have been trained to look for. For years, the advice has been consistent: before you sign in anywhere, check you are on the genuine website. Look at the URL. Confirm the padlock is there. Make sure the address is exactly right. That advice remains sound. The problem is that attackers have found a way to work around it entirely, using an attack where the final login page genuinely is Microsoft’s.
How Real Login Page Phishing Works
The attack exploits a legitimate Microsoft feature called device code authentication. This feature exists to help devices that do not have a conventional keyboard, such as smart televisions, meeting room displays, or certain business equipment, authenticate to a Microsoft account. Rather than typing a password directly on the device, the user enters a short code on a separate device that is easier to use. Microsoft matches the code to the device and grants access.
Attackers have found a way to misuse this process. They generate a device code of their own and then contact potential victims with a message designed to create urgency. The message might appear to be a legal notice, a shared document notification, an urgent account alert, or any other scenario that encourages the recipient to follow a series of steps. At some point in those steps, the victim is directed to Microsoft’s genuine sign-in page and asked to enter a short code.
The website is real. The login page is real. The URL is correct. The padlock is there. Every visual indicator that has historically been used to confirm legitimacy is present. The code itself looks harmless because the user is on a genuine Microsoft page. However, entering that code does not prove the user’s identity to Microsoft. It grants the attacker’s device permission to access the account.
From that point, the attacker can read emails, access files in OneDrive and SharePoint, view Teams conversations, and move through connected systems, all without ever knowing the victim’s password. The account access may persist even after the user has logged out of their own session, because the attacker’s device has been granted authorisation rather than using a stolen credential that can be changed.
This is the same category of threat covered in our earlier article on device code phishing, now appearing with increased frequency and in more convincing forms. The underlying mechanism is identical, but the delivery is becoming more sophisticated.
Why Traditional Warning Signs Do Not Apply
The challenge real login page phishing presents is that it strips away most of the indicators that awareness training teaches people to look for.
There is no fake website. There is no slightly misspelled domain. There are no suspicious links to hover over or visual inconsistencies to spot. The page the victim ends up on when they enter the code is exactly the page it claims to be. Even someone who checks the URL carefully, confirms the padlock, and compares the address with what they expect will find nothing wrong, because everything they are looking at is genuine.
Multi-factor authentication, which is one of the most effective protections against conventional credential theft, may also provide incomplete protection in this scenario. Because the victim completes the authentication themselves on a genuine Microsoft page, the system treats the login as fully verified. The user has effectively told Microsoft that the device access is legitimate, even though they did not understand what they were authorising. Our article on strengthening your business security covers why multi-factor authentication remains essential even though it is not a complete defence against every attack type.
For businesses in Brighton and across Sussex that have invested in phishing awareness training, this is an important development to communicate. Staff who have been trained to look for fake websites may feel confident that they checked, saw a genuine Microsoft page, and proceeded safely. That confidence is misplaced in this specific attack because the threat is not in the page they are looking at. It is in what the code they are entering is authorising.
The One Question That Stops This Attack
The single most effective protection against real login page phishing is a habit rather than a technical control. Before entering any code on a Microsoft login page in response to an unexpected email or message, pause and ask one question: did I start this process?
Legitimate device code authentication is initiated by the user when they are trying to sign into a device that cannot accept a password directly. The flow begins with the device displaying a code and asking the user to go to a specific address to enter it. It is a process the user deliberately initiates.
If a code arrives in an email, a Teams message, or through any other incoming channel without the user having started a device authentication process themselves, that code should not be entered anywhere. The presence of a genuine Microsoft login page at the end of the process does not change this. The question is not whether the page is real. The question is whether the user started the process that led to it.
This habit requires no technical knowledge and no visual assessment. It works regardless of how convincing the surrounding email or message appears and regardless of how genuine the final login page looks. Did I start this? If the answer is no, stop.
Communicating This to Your Team
Making this understanding widespread across a business requires updating how phishing awareness is communicated. The traditional message, check the URL and look for a fake website, is insufficient for this attack and may actually create a false sense of security. A team member who checks the URL, sees a genuine Microsoft domain, and proceeds may believe they have done everything right.
The updated message adds a critical layer: a genuine website is not the same as a safe action. The safety of an authentication step depends on whether the user initiated it, not on whether the page they end up on is real. This is a subtle but important distinction that requires explicit communication rather than being self-evident.
A brief team communication explaining how this attack works and introducing the one key question takes only minutes. Our article on employee cyber security awareness covers how to build current and relevant security awareness into regular team practice without it feeling like a burden.
Technical Steps Worth Taking Alongside Awareness
Staff awareness addresses the behavioural dimension. Technical measures can further limit the exposure this attack creates.
Microsoft 365 administrators can restrict or disable device code authentication for accounts where it is not needed for operational purposes. For most business accounts, there is no legitimate need to use this authentication method in day-to-day work. Disabling it removes the attack vector entirely for those accounts.
Where device code authentication cannot be disabled, conditional access policies can restrict which devices and locations are permitted to complete this type of authentication. This does not prevent the attack from being attempted but limits the circumstances under which it can succeed.
Our managed IT services include Microsoft 365 security configuration reviews for businesses across Sussex and the South East, covering settings like these that are often left at default and that create unnecessary exposure to current attack methods.
What This Means For Businesses
Real login page phishing represents the continued evolution of attacks toward exploiting genuine systems rather than building convincing fakes. The traditional advice to verify the website is still worth following. However, it is no longer sufficient on its own, and businesses that rely on it as the primary defence are more exposed than they realise.
For business owners and directors, the practical response involves two things. First, update the awareness your team has about phishing. Explain specifically that this attack exists, that it uses a genuine Microsoft page, and that the one question to ask is whether the user initiated the process they are being asked to complete. Second, ask whoever manages your Microsoft 365 environment to review whether device code authentication can be restricted for accounts where it is not operationally needed.
Final Thoughts
The security advice that worked well in the past needs to evolve as attacks evolve. Checking for a fake website was always the right instinct. The instinct to stop and ask whether you started a process is the next layer that current attacks make necessary.
Share the question with your team: did I start this? Make it a reflex before any code is entered on any login page that arrived through an unexpected email or message. That habit, applied consistently, removes most of the leverage this attack relies on.
What is real login page phishing?
Real login page phishing is an attack where the victim is directed to a genuine Microsoft authentication page and asked to enter a code that was generated by the attacker. Entering the code grants the attacker’s device access to the victim’s Microsoft account without any password being stolen. The login page is completely genuine, which removes the visual warning signs that traditional phishing awareness training focuses on.
Why does multi-factor authentication not always protect against this attack?
Multi-factor authentication is designed to confirm that the person logging in is who they claim to be. In this attack, the victim completes the authentication process themselves on a genuine Microsoft page, so the system treats the login as fully verified. The victim has inadvertently authorised the attacker’s device, telling Microsoft the access is legitimate. Technical controls still help, but the attack can succeed even when multi-factor authentication is active if the victim completes the process themselves.
What is the one question that stops this attack?
Before entering any code on a Microsoft login page in response to an unexpected email or message, ask: did I start this process? Legitimate device code authentication begins when the user initiates sign-in on a device that cannot accept a password directly. If a code has arrived unexpectedly from an external source, the user did not start the process, and the code should not be entered regardless of how genuine the login page appears.
Can Microsoft 365 be configured to reduce the risk from this attack?
Yes. Microsoft 365 administrators can restrict or disable device code authentication for accounts where it is not needed operationally. Conditional access policies can also limit which devices and locations are permitted to use this authentication method. For most business accounts, device code authentication is not required for day-to-day work, and restricting it removes the attack vector for those accounts entirely.
How is this different from the device code phishing covered in an earlier article?
The underlying mechanism is the same: attackers exploit Microsoft’s legitimate device code authentication feature to gain account access without stealing a password. What has changed is the frequency and sophistication of delivery. The attack is appearing more often, the emails used to initiate it are becoming more convincing, and the surrounding context is being crafted more carefully to create urgency and reduce the chance that the recipient pauses to question what they are doing.